Vendor compliance for university DPOs, IT, procurement & the library
Stop emailing vendors.
Send them one link.
The vendor uploads their documents once. The AI checks everything against GDPR, the EU AI Act, data-residency rules and your own internal policies. You get a traffic-light report and decide.
One review. Four teams. Zero duplicate questionnaires.
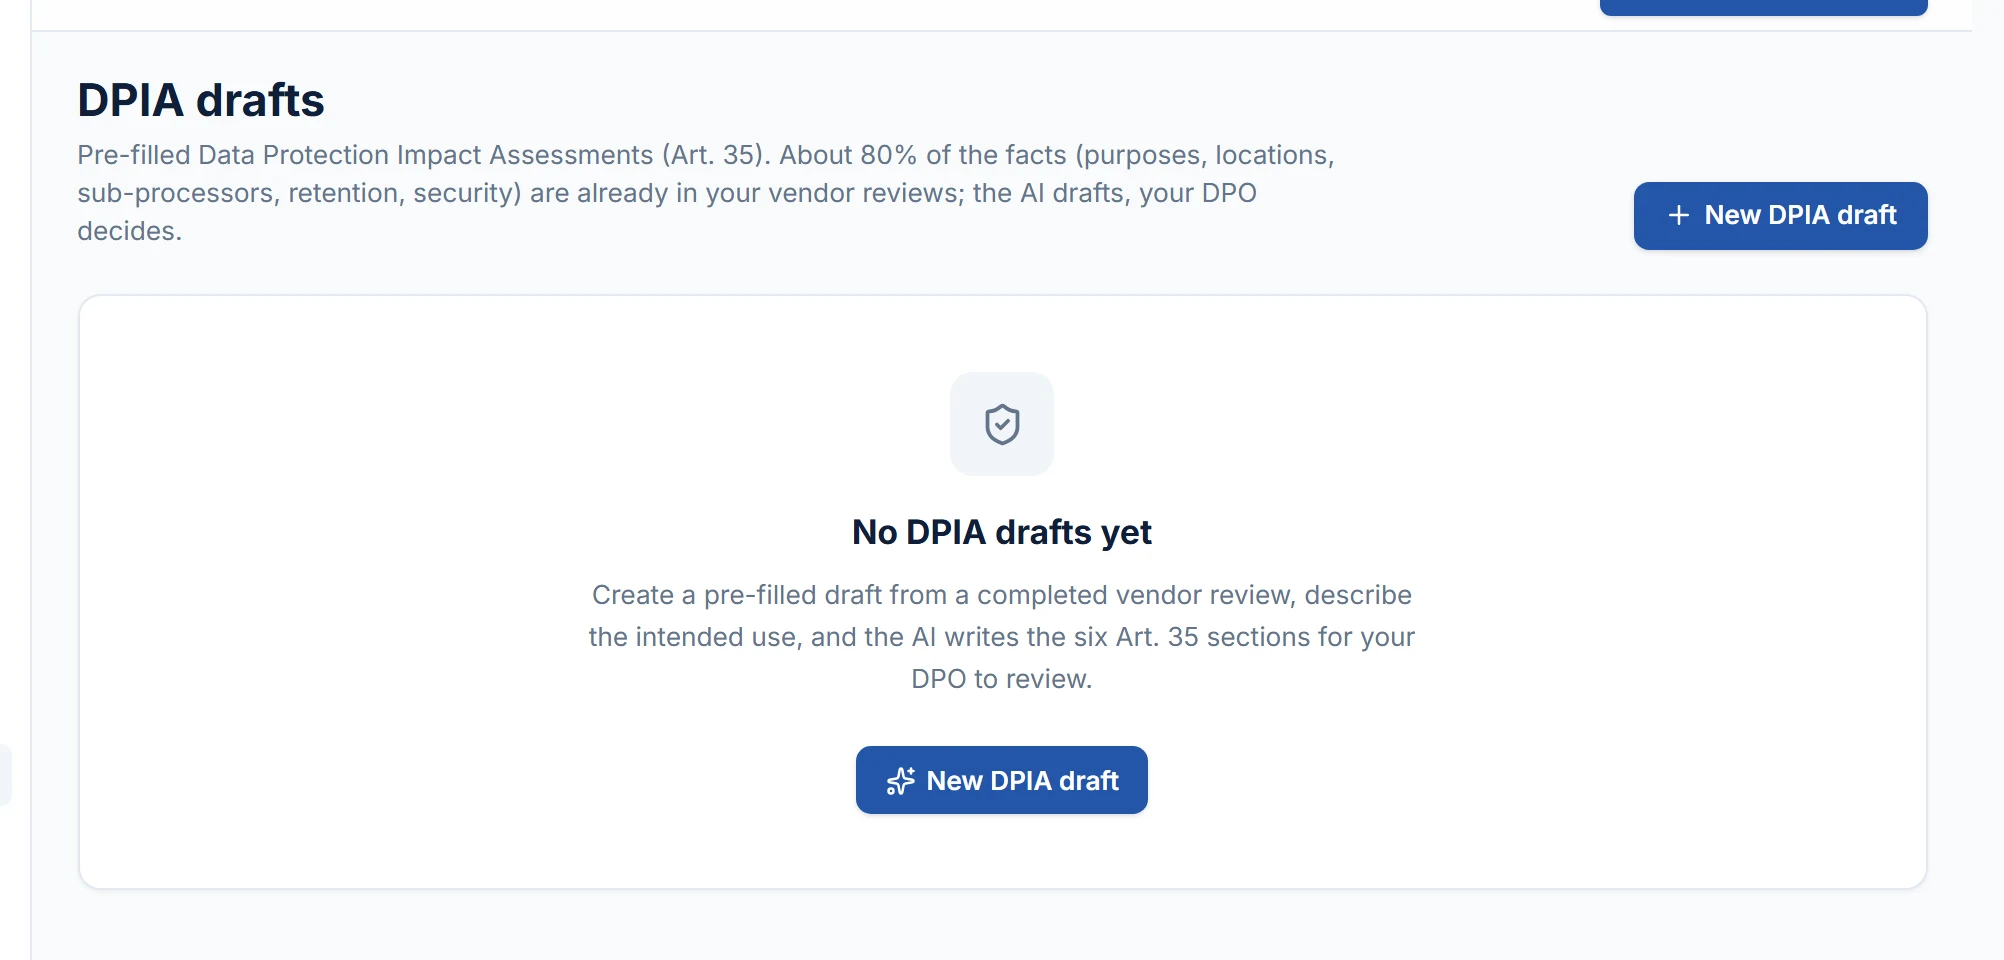
Every Art. 28 answer, already cited
GDPR, AI Act and transfer checks arrive pre-analyzed with the source attached, and DPIA drafts start themselves from finished reviews. You sign decisions instead of chasing attachments. The DPA is drafted and signed on the same review, amendments included.
Security answers you can actually verify
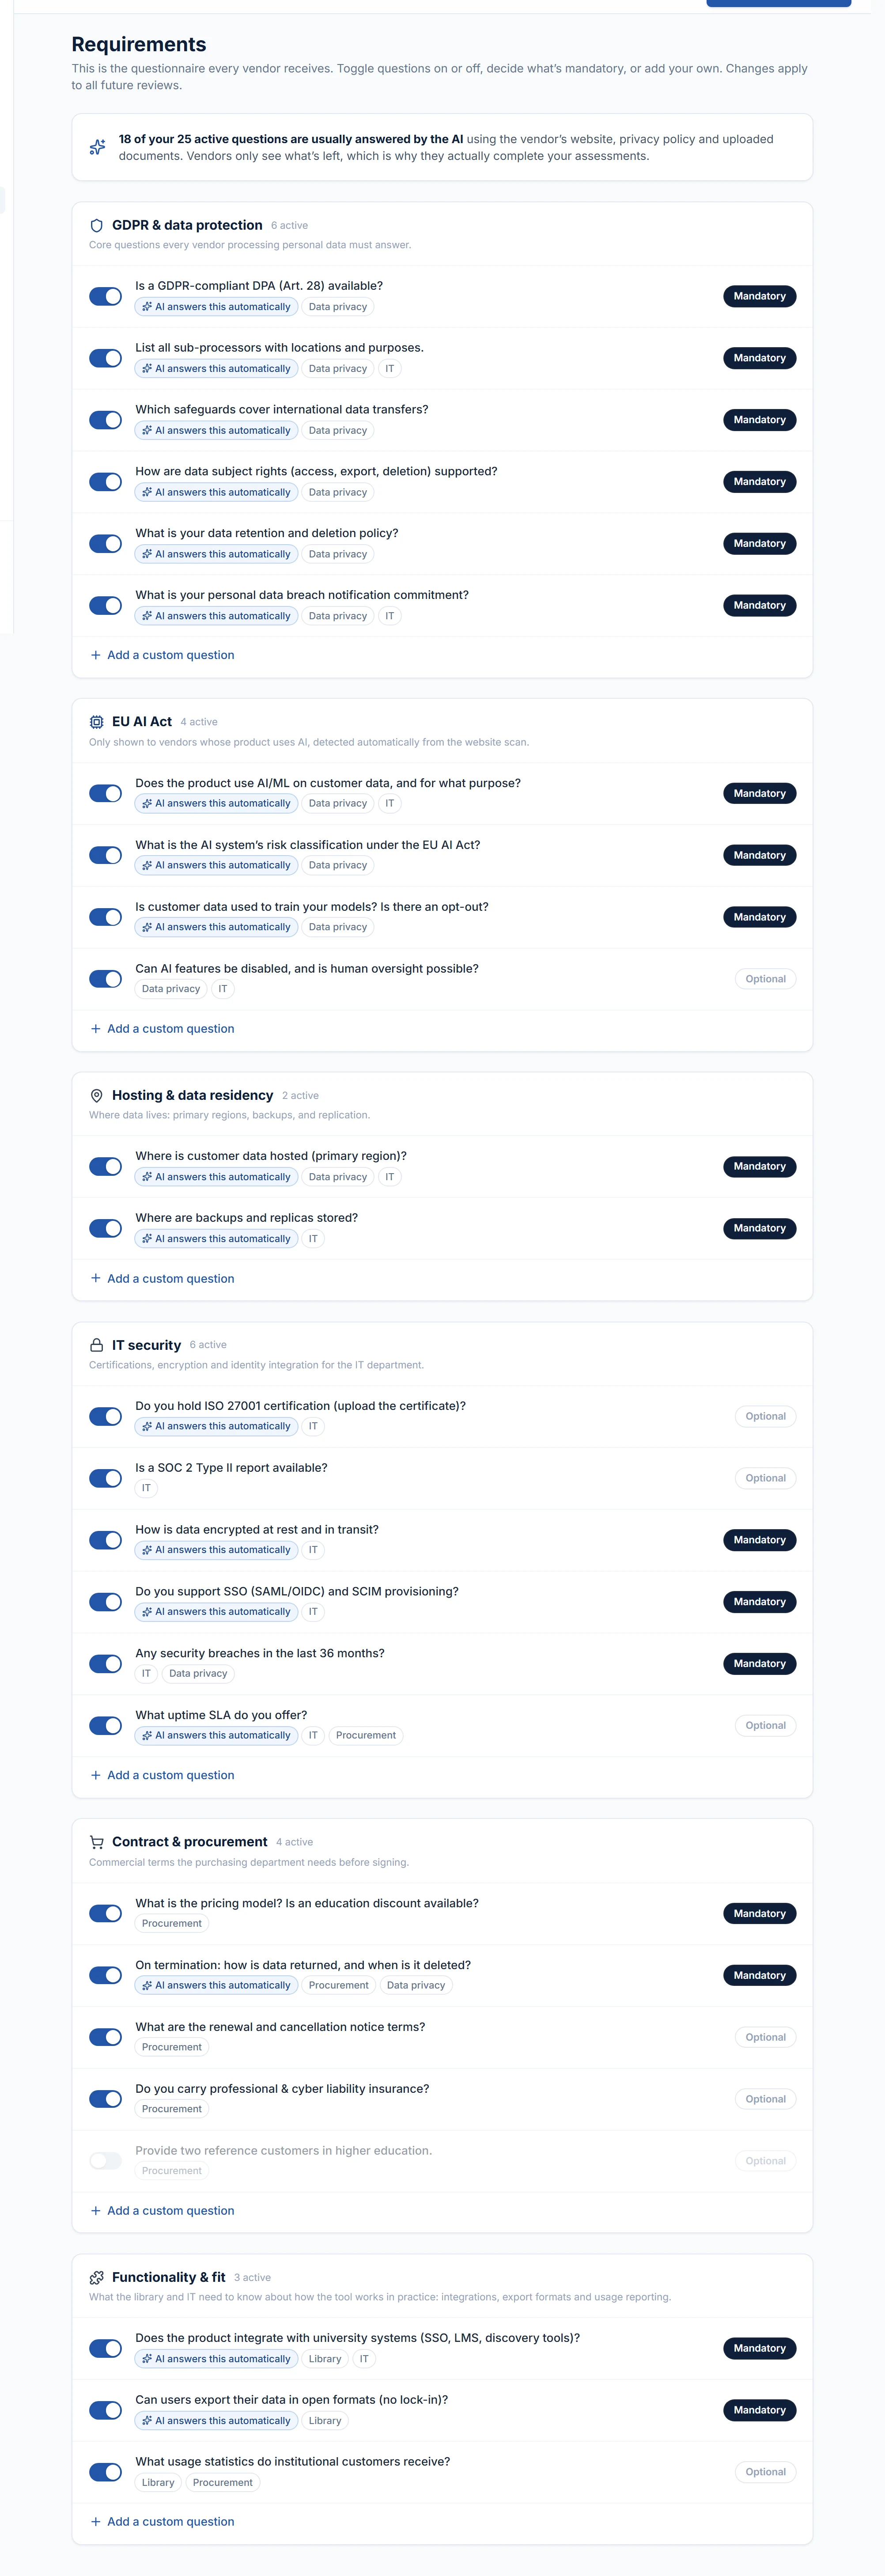
ISO 27001, encryption, SSO and breach history are extracted from the vendor's own documents and checked against your requirements. The 40-tab spreadsheet retires.
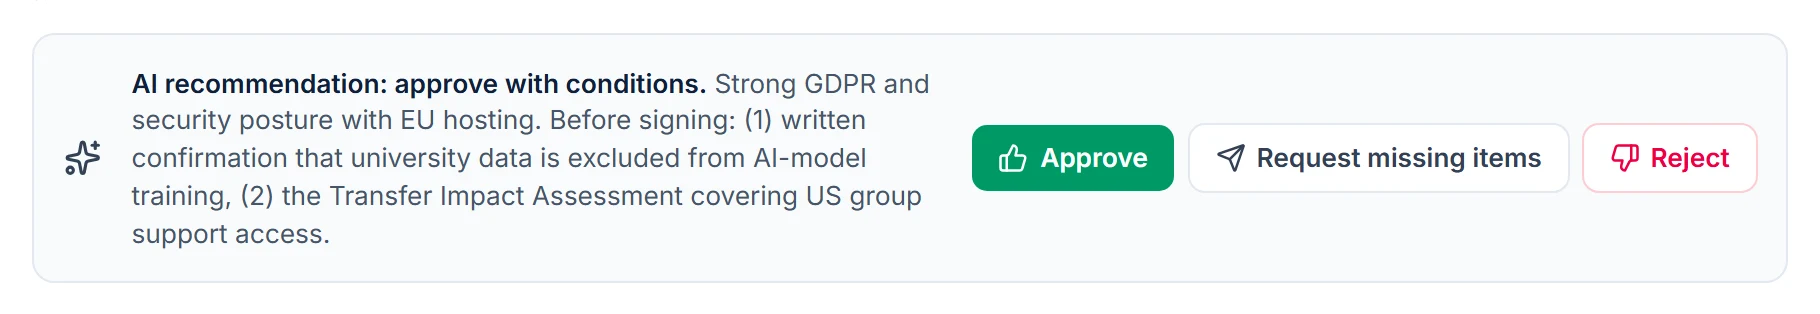
A defensible decision on record
Exit terms, renewal traps and the prices you were actually quoted sit beside the compliance verdict. Approve with an audit trail that still answers questions years later.
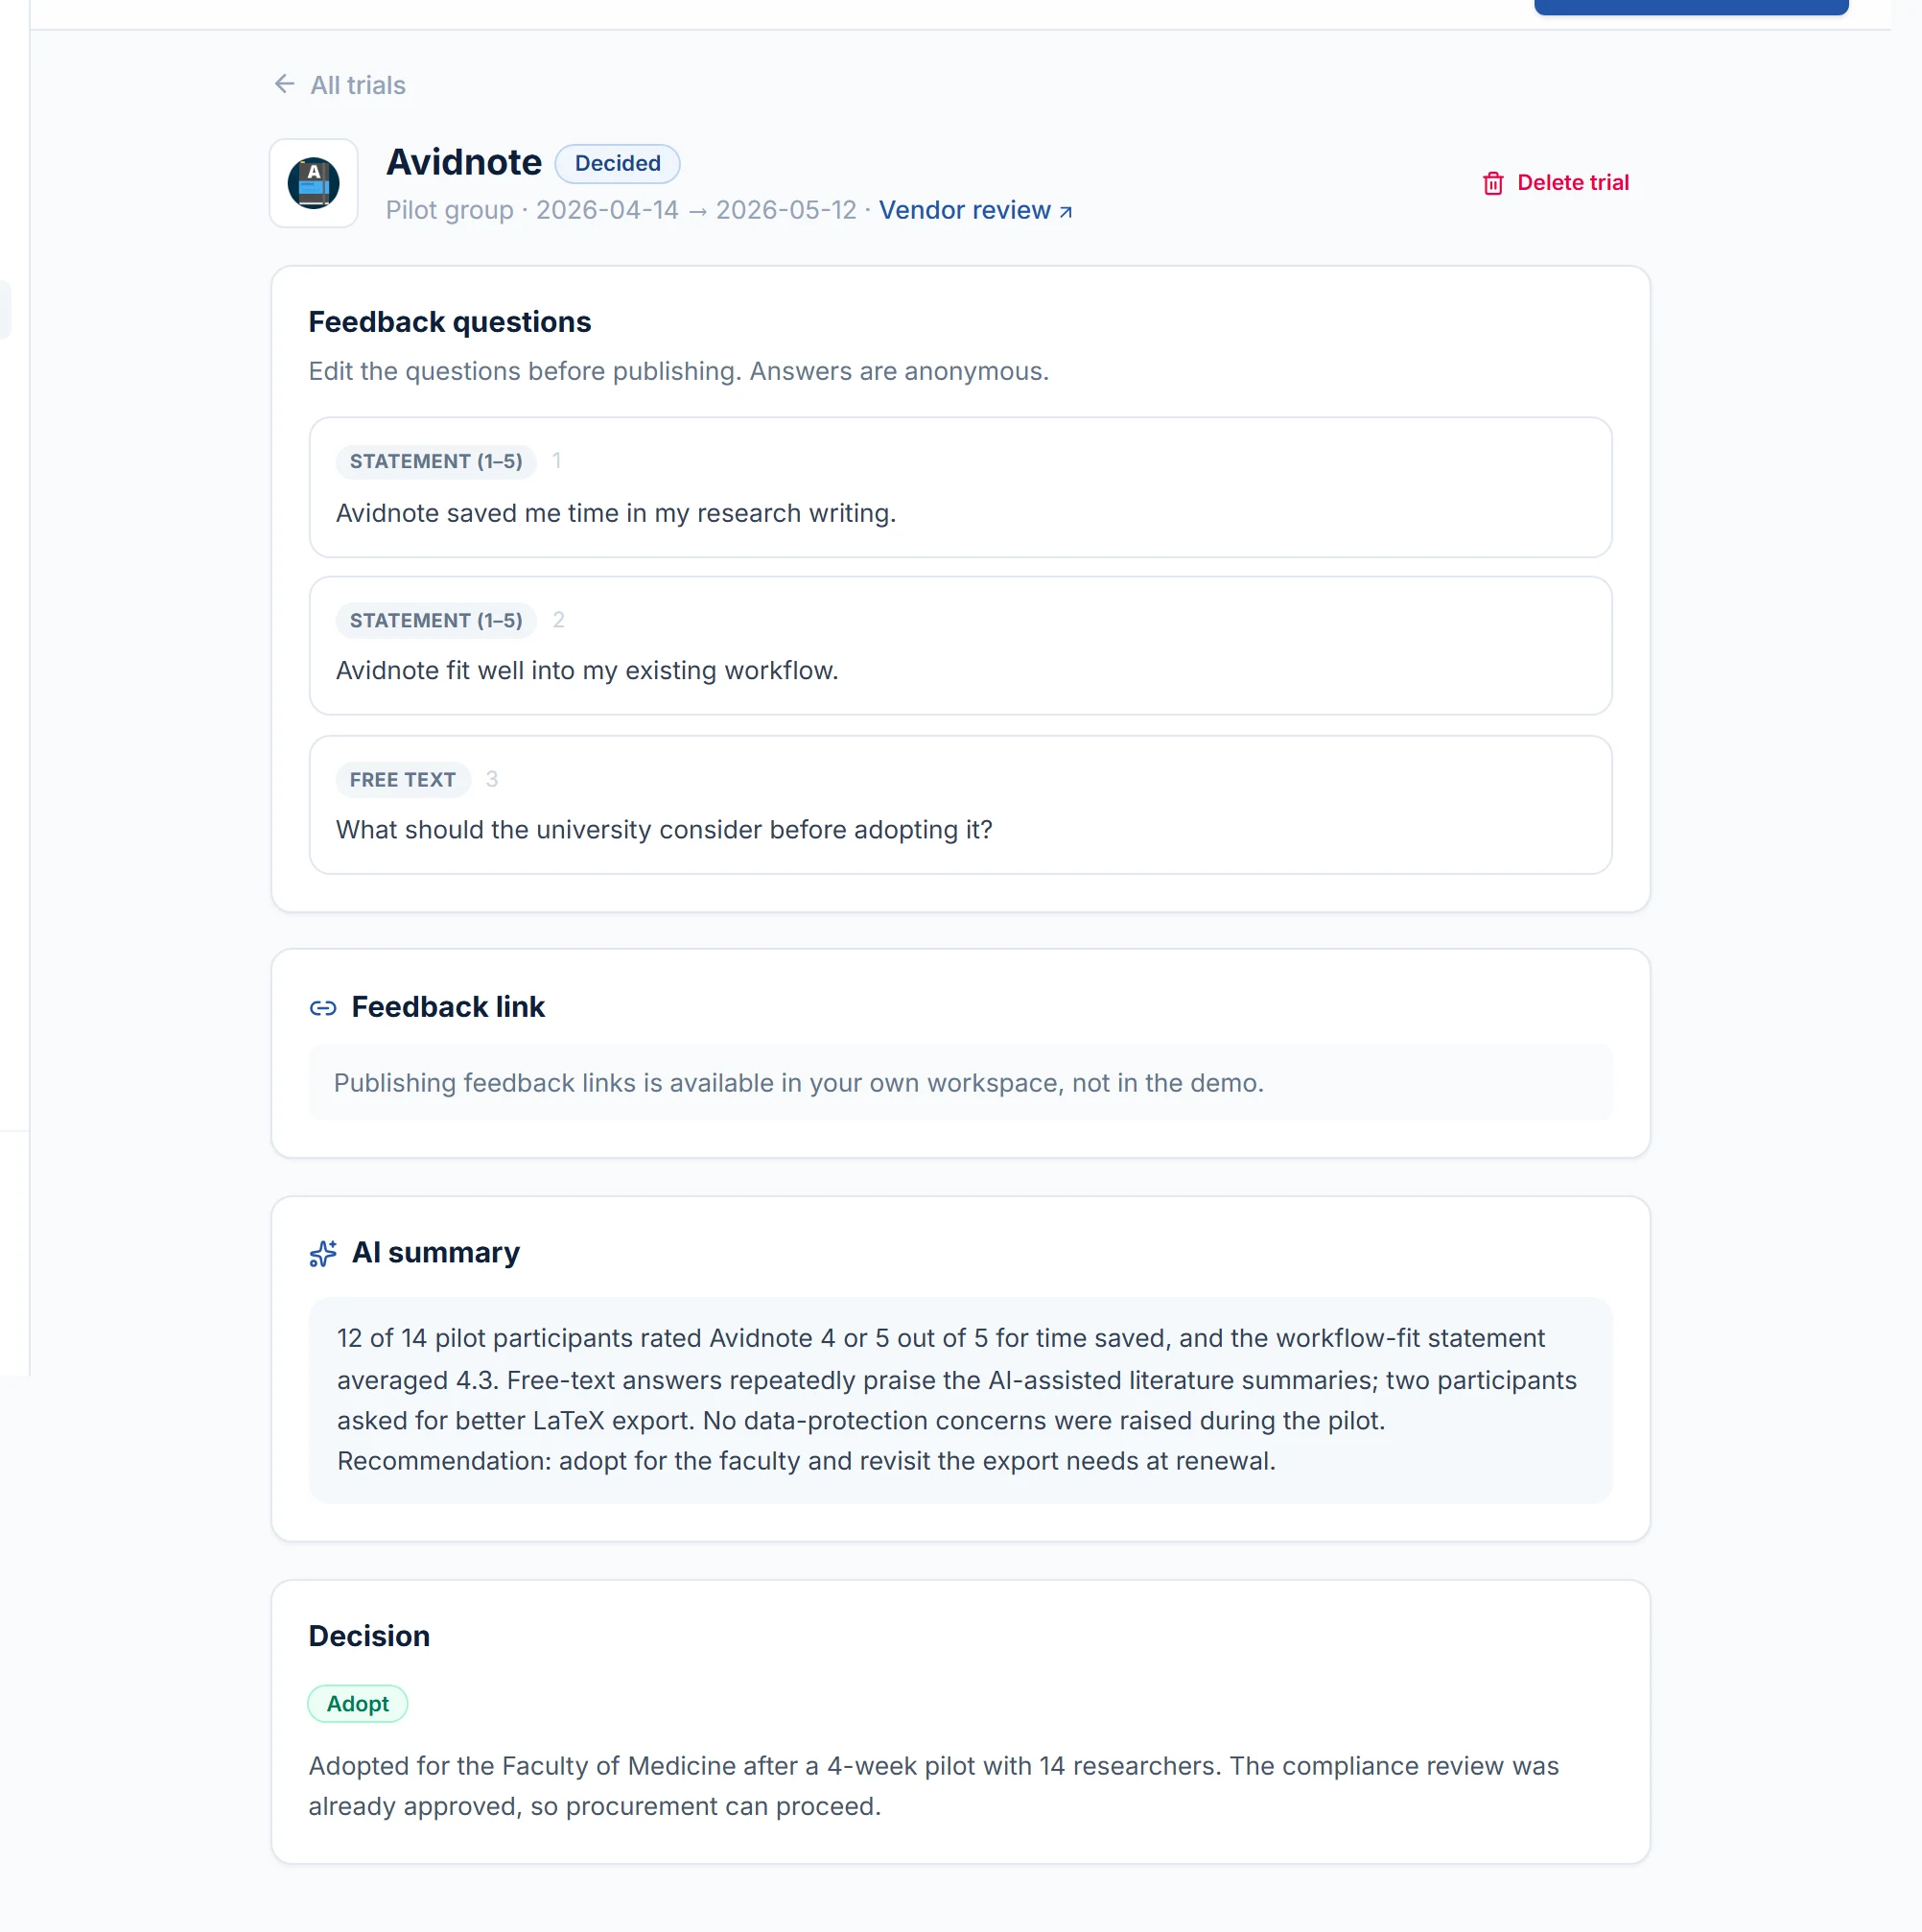
Tool trials that reach a decision
Run pilots with anonymous feedback links, compare functionality and accessibility side by side, and adopt tools with the compliance box already ticked.
Stop chasing vendors. Send one link.
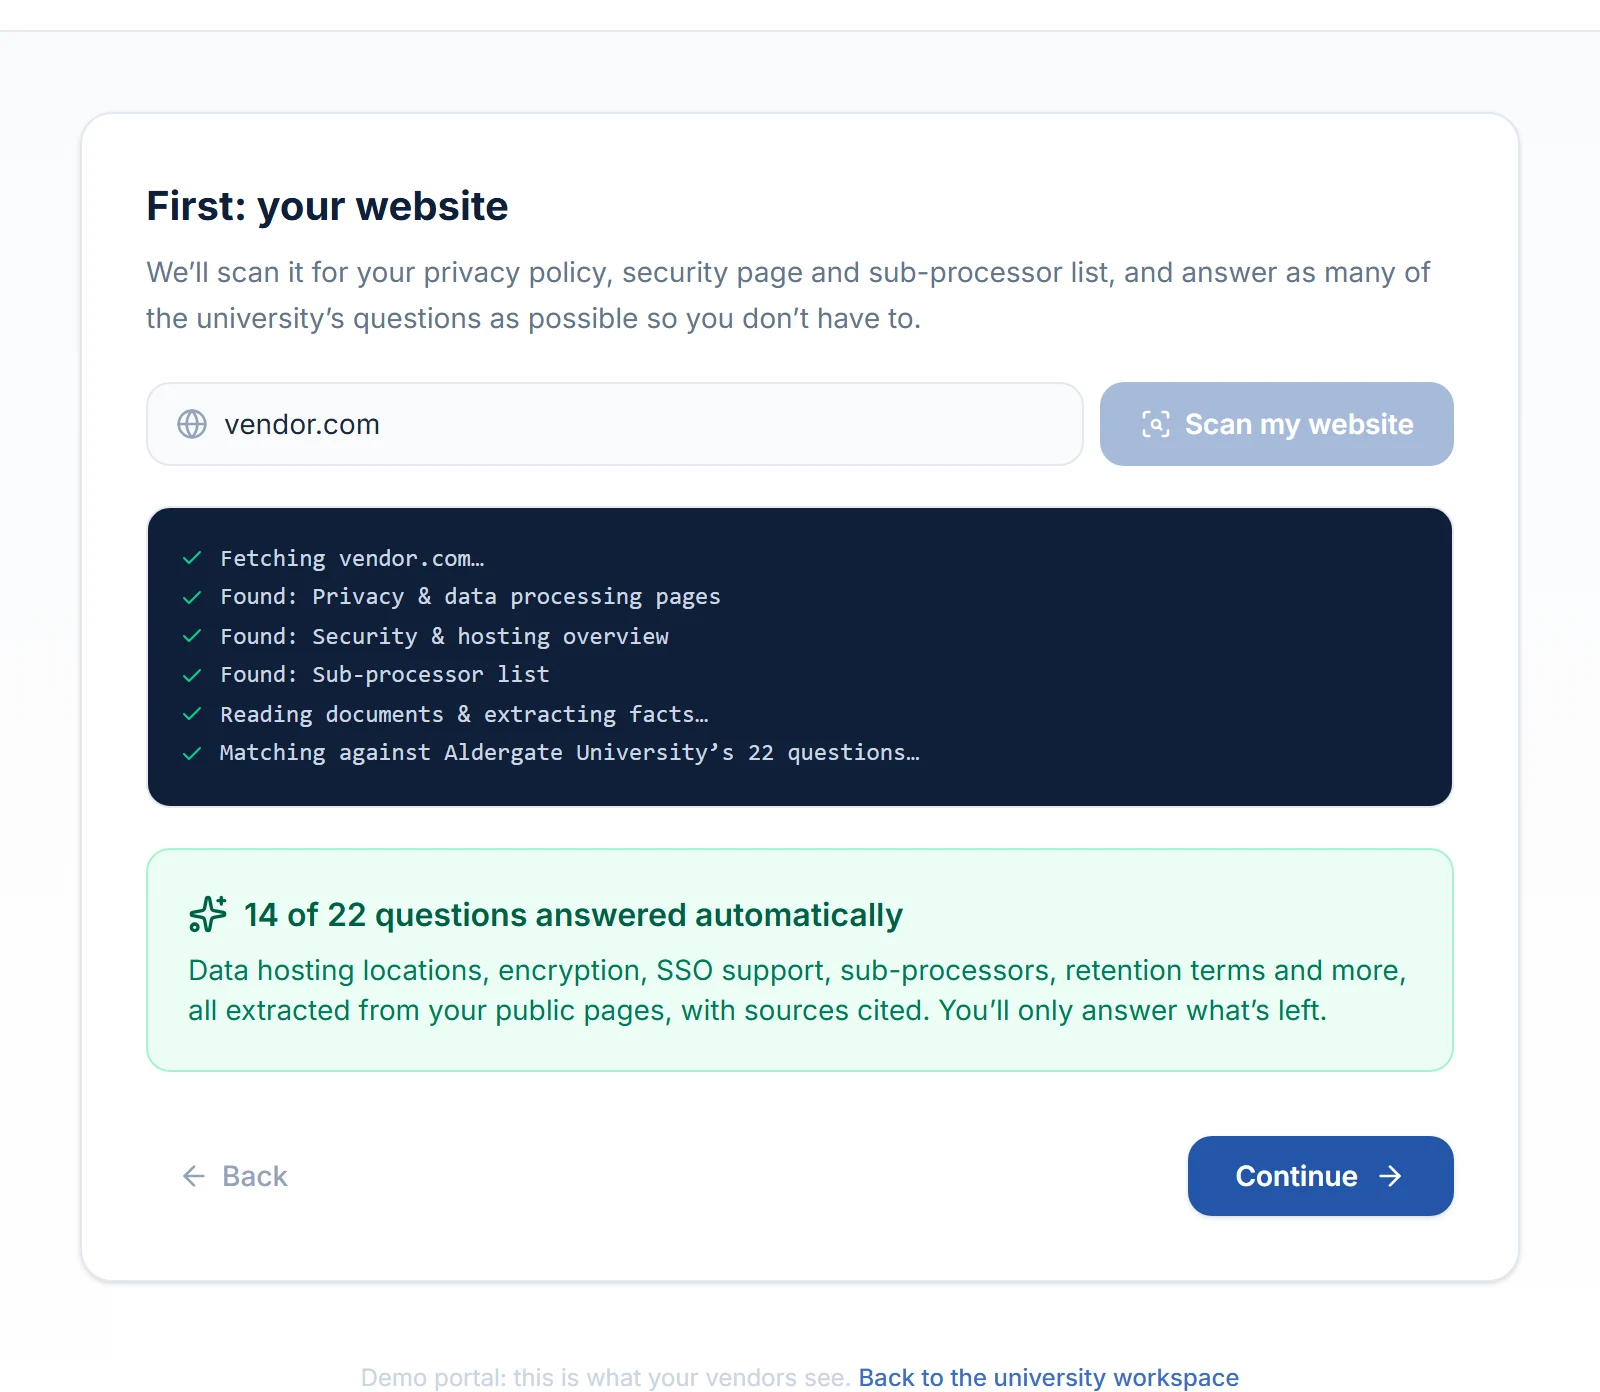
The vendor pastes their website, and the AI reads their public privacy and security pages, pre-filling most answers with sources. They finish in minutes, so they actually finish.
- No vendor account needed, ever
- Most answers pre-filled from the vendor's public pages and documents
- GDPR, the EU AI Act and your own policies in one questionnaire
A traffic-light verdict, not a pile of PDFs
Every answer becomes a pass, needs-attention or gap check with a plain-language note and a cited source. Four teams read one report and decide.
- Every check traces back to a document or page
- Open items become a one-click request to the vendor
- Export a decision memo for the file
Choosing between two tools? Compare them like your auditor would.
When a department wants "a survey tool" there are always three candidates. Validemic puts completed reviews side by side (compliance verdicts, commercial terms and your actual quoted prices) so the decision meeting takes ten minutes, not another round of emails.
Compliance, side by side. GDPR, EU AI Act, hosting and AI-training stance: every verdict aligned in one table, with sources one click away.
Real prices, not list prices. Vendors rarely publish site-licence pricing. Upload the quote you received and the AI extracts the figures, or type them in yourself. They stay in your workspace.
A defensible decision. The comparison is built from cited assessments, so "why did we pick this one?" has an answer years later.
Functionality for the library. Integrations, export formats and accessibility sit in the same table as the compliance verdicts, so the library compares tools where IT and the DPO already are.
- A researcher wants a new tool → someone emails the vendor.
- “Where do you store data? Can you send your privacy policy?” Repeated for every vendor, by every department.
- Weeks of back-and-forth. Attachments scattered across inboxes.
- Someone reads a 40-page privacy policy line by line.
- IT, procurement and the DPO each ask the vendor separately.
- You send one link. The vendor uploads documents and answers on their side, with no account needed.
- The AI pre-fills most answers from the vendor’s website and documents, so vendors actually finish it.
- Every answer is checked against GDPR, the EU AI Act, data residency and your internal policies, with sources cited.
- One review serves all three teams: privacy, IT and procurement see what’s relevant to them.
- You decide in one click: approve, request missing items, or reject.
What that actually saves you
Deliberately conservative numbers, based on what a single email-based vendor assessment costs a university today.
Reading policies, chasing attachments and answering the same questions across privacy, IT and procurement takes 7–8 staff hours per vendor. With pre-filled answers and cited checks, reviewing takes about an hour.
Email-based assessments typically run 3–5 weeks. Vendors finish the Validemic portal in minutes, and your three teams review one shared report instead of three inboxes.
Assuming a conservative 30 vendor reviews per year, 6 hours saved per review and a fully-loaded staff cost of €50/hour. Most universities review more vendors than that.
Estimates err on the low side on purpose. Savings from faster procurement, avoided duplicate licences and reduced compliance risk are not included.
From request to decision in three steps
Designed so the university does almost nothing, and the vendor does almost nothing either.
Send the link
Type the vendor’s name and email. Validemic generates a secure assessment link with your university’s questions. Mandatory and optional ones are clearly marked.
The AI does the reading
The vendor pastes their website. The AI finds their privacy policy, security page and sub-processor list, and pre-fills most answers. It also spots the analytics, chat and tracking services embedded on the site and flags any missing from the sub-processor list. The vendor uploads the rest, explains the gaps and submits.
You get a verdict, not PDFs
Every answer becomes a pass / needs-attention / gap check against GDPR, the EU AI Act, and your own policies, each with a plain-language explanation and cited source.
Everything compliance work needs, nothing it doesn’t
GDPR checks
DPAs, sub-processors, transfers, retention and breach terms are mapped to the articles automatically, with the source cited. The website scan also flags third-party services embedded on the site that are missing from the sub-processor list.
EU AI Act classification
Detects whether a product uses AI, classifies its risk level, and flags training-on-your-data clauses hidden on page 11.
Data residency
Primary regions, backups and every sub-processor location, verified from documents rather than marketing pages.
Your internal policies
Upload your own policy documents. Every vendor is checked against your rules, not just the law.
Customizable questionnaire
Toggle questions, set mandatory vs. optional, add your own. AI-answerable questions never reach the vendor.
AI assistant
A chat that knows your vendors, documents and the legislation. Ask “Is this Schrems II compliant?” and get a sourced answer.
DPA e-signing
Draft the Art. 28 agreement from a template or upload the vendor’s, then both parties sign in the same place: typed, drawn or an uploaded signed copy. A new sub-processor becomes an amendment both sign again, with the history kept.
Change monitoring
Vendor privacy policies, DPAs, sub-processor lists and regulation texts are re-read daily. When something changes, your team gets a plain-language summary by email.
DPIA drafts
Start an Art. 35 impact assessment from a finished review: purposes, locations, sub-processors and retention are already extracted and cited. The AI drafts, your DPO decides.
Your administration has better things to do
Book a demo and see Validemic on your own vendors, or explore the demo workspace with a fully assessed vendor, including the portal your vendors would see. Validemic is also free with an Avidnote or Kahubi site license.